Five safety steps to take before you vibe code
Building apps with AI calls for security habits, from keeping API keys out of prompts to rate limiting and reviewing the code.
The facts
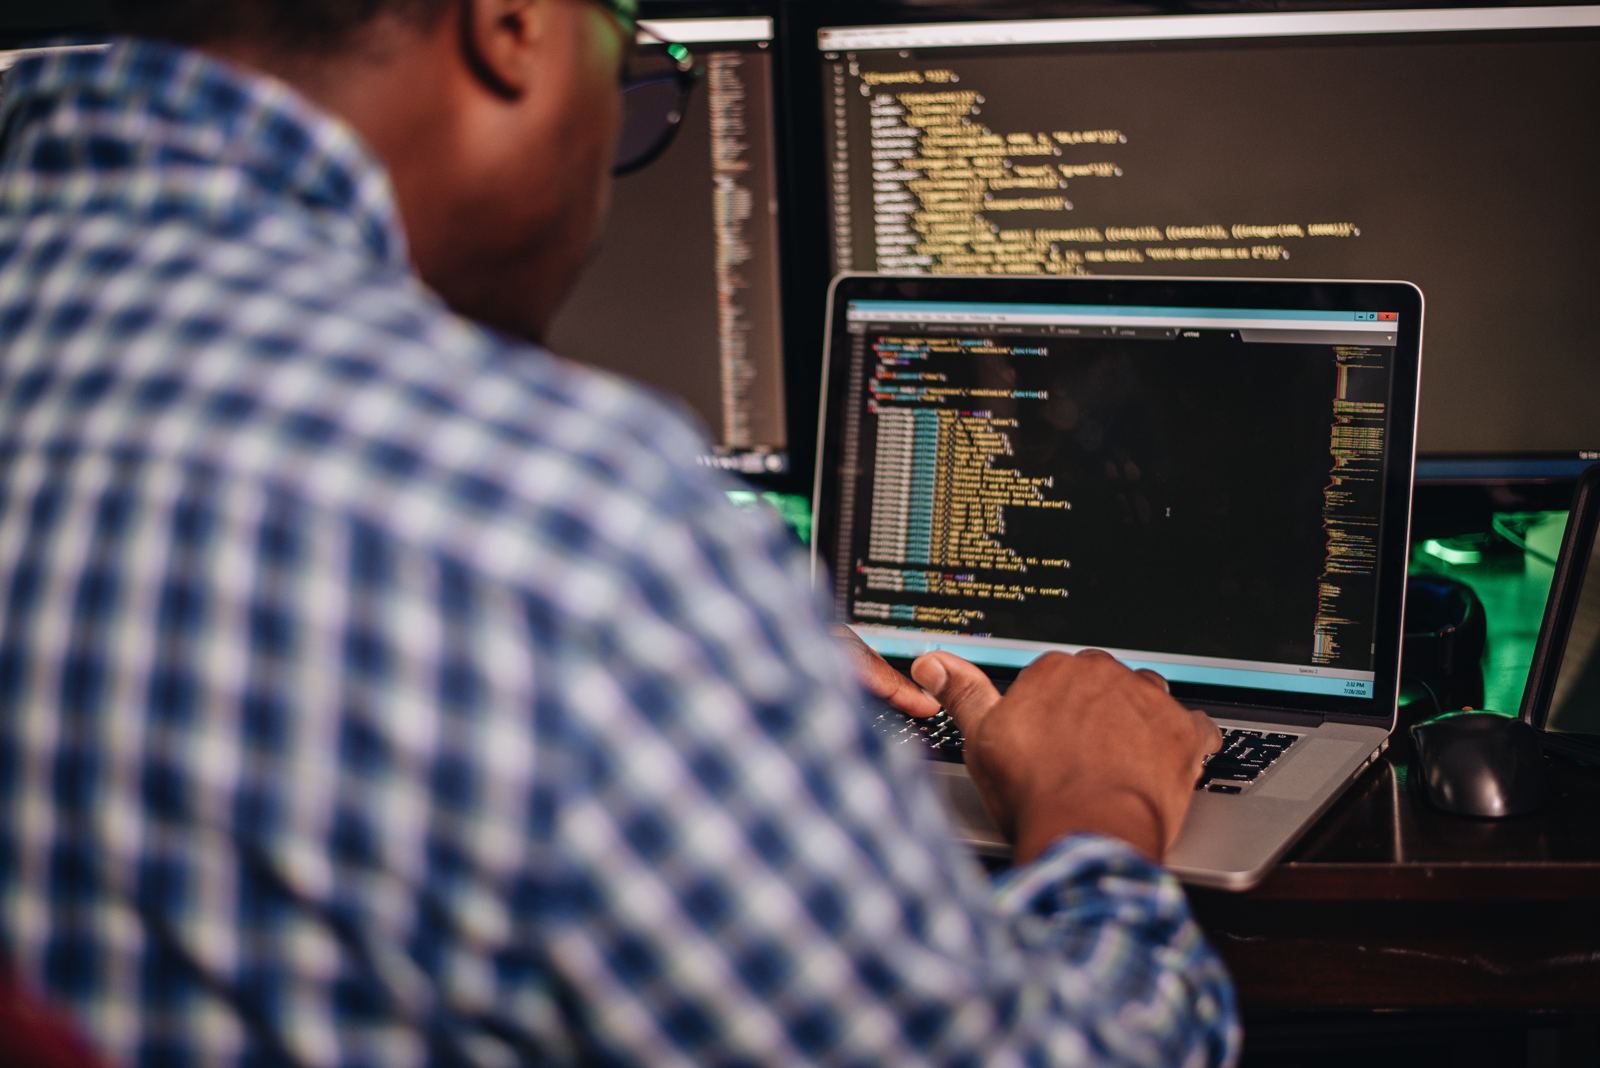
- According to Engadget, vibe coding is now the new normal in the tech industry, after Andrej Karpathy described coding by talking to an AI model in an X post.
- Engadget says the security firm Apiiro studied Fortune 50 companies and found engineers were four times more productive but produced ten times the number of security issues.
- The advice includes spelling out security requirements in prompts, never pasting API keys or passwords into a prompt, and storing secrets in environment variables or a password manager.
- Engadget also recommends parameterised SQL queries, rate limiting, and having a professional or other AI tools review the code, naming tools such as TruffleHog and the OWASP Top 10 list.
Case notes · Danny's take
Why it matters
Speed is the selling point of vibe coding. The cost is code nobody on your team has read. If an AI cuts corners and you don't check, the weak spot ships with your app. That's a real risk for solo builders in Lagos or anywhere else who are building for real users without a security team behind them. Fast is not the same as safe.
For builders
Write your security rules down once in a context file, keep secrets out of prompts and out of your GitHub repo, and run a scanner before launch. Treat the AI's code like a junior developer's first draft: useful, but never trusted until reviewed.
Not financial advice. Do your own investigation.
This story was summarised with AI from Engadget's reporting and checked against our editorial policy. Danny's take reflects his views. Disclaimer.
Danny Walter
Founder of Moon Republic, Volt Terminal and Moon Republic Academy. Author of The Market Is a Crime Scene and After the Applause.